Rerun

Control Who Has Access to Your Apps

Get access reviews that catch missing MFA, leavers still signed in and risky app grants, and accounts set up by role for every new hire.

Control Who Has Access to Your Apps agent board

About

An access admin that keeps the right people on the right access, from day one to their last day, with every change shown to you first.

What it does

  • Runs access reviews: accounts without MFA, inactive or departed people still active, admin rights to reduce
  • Flags risky third-party app grants and secrets or certificates about to expire, with the owner of each action
  • Prepares accounts, groups and roles for new hires from your role matrix
  • Lists everything to remove when someone leaves or goes inactive, and opens the revocation tickets
  • Keeps a history so each weekly review shows what changed

What you need

  • Nothing to start: a user export from Google Workspace, Okta, Entra ID or AWS IAM is enough for the first review
  • Jira (optional) to open access and revocation tickets for IT; it works with your own tracker instead
  • It can work in your admin console from its own computer, once you sign in

How setup works

You get a first access review in the first minutes. It then learns your access rules and team roles, connects your tracker if you want, and sets up a weekly review.

What stays in your hands

  • No account, role, app grant or key is created, changed or removed without your go-ahead
  • You see the exact change set before anything is applied

What you will need

  • Jira

Coworkers in this template

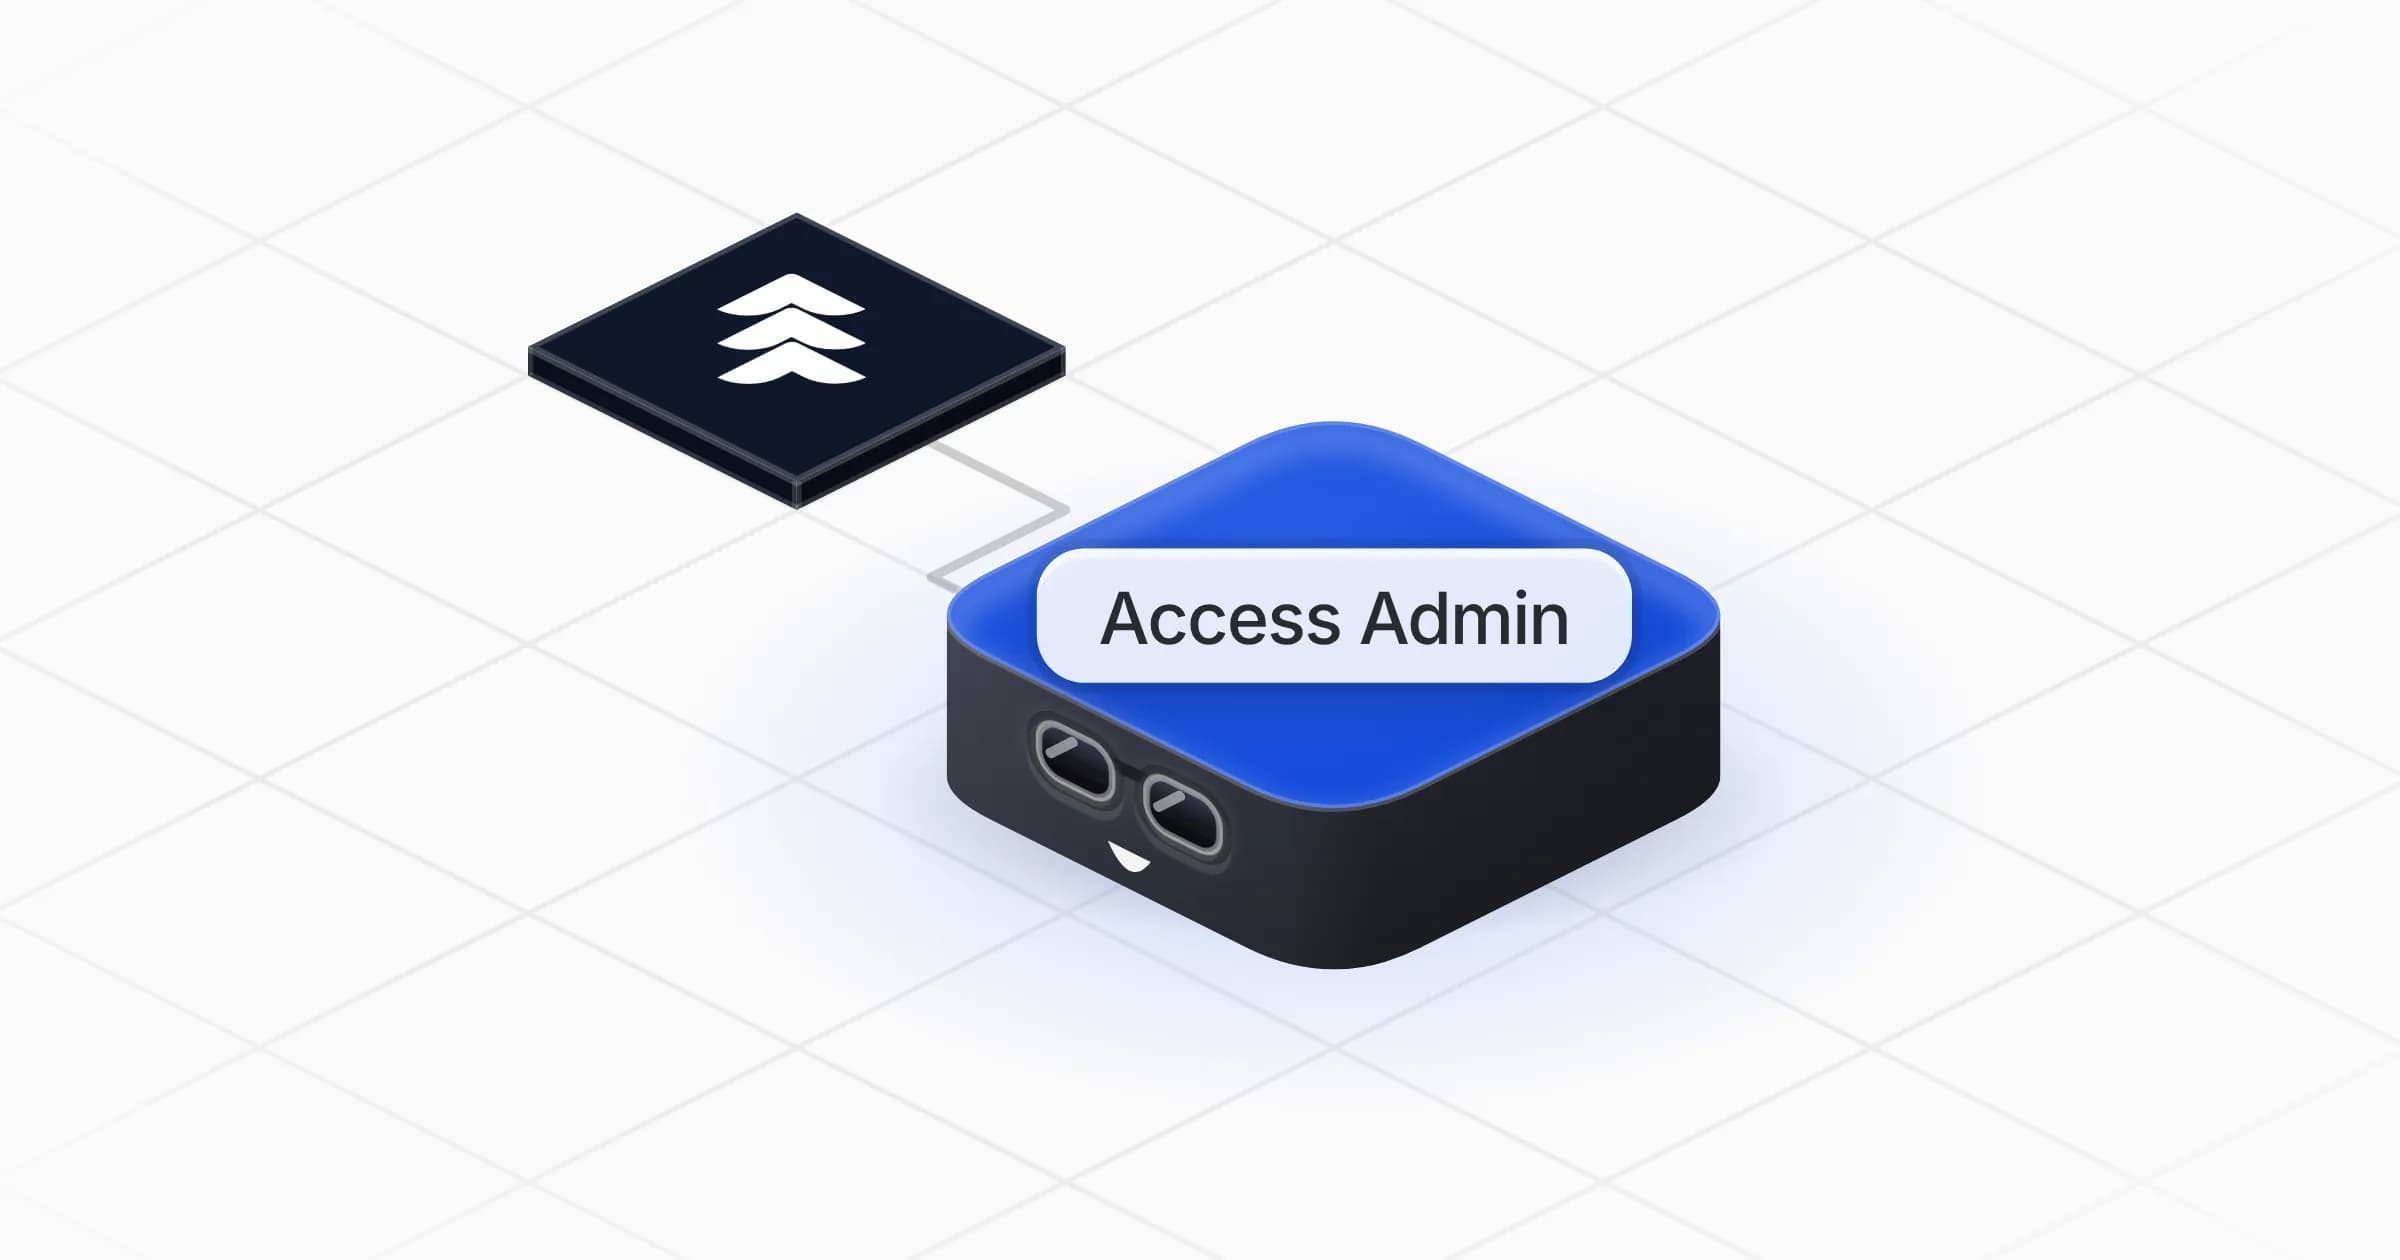
Access Admin

Keeps the right people on the right access: accounts by role for joiners, clean removal for leavers, and weekly access reviews.

Apps

Skills · 6

Assign roles by team

Use when asked to assign roles, groups or apps based on a person's team or org unit, to build or update the role matrix, or to handle someone changing team.

Check third-party app grants

Use when asked to review the OAuth or third-party apps that have access to the user's accounts, to spot risky permissions, or to say what changed in app grants.

Create new accounts

Use when asked to create user accounts in the identity provider, to onboard a new hire, or to provision access from a form, a sheet, an HR record or the directory.

Revoke leavers' access

Use when asked to remove access for someone leaving, to check the HR list of leavers or inactive employees against active accounts, or to open the revocation tickets.

+2 more

Scheduled tasks · 1

Weekly access review

At 09:00 AM, only on Monday
Frequently asked questions

Which identity providers does it work with?

Google Workspace, Okta, Entra ID, AWS IAM and others: it works from a user export, or in your admin console from its own computer once you sign in.

Will it suspend accounts on its own?

No. It shows the exact list of changes and applies them, or opens the tickets, only after you approve.

Can it set up accounts for new hires?

Yes. It prepares the account, groups, apps and roles from your role matrix, shows the change set, then creates them in your console or opens the IT ticket.

Does it check third-party OAuth apps?

Yes. It compares granted apps to your approved list, looks at the scopes they hold and flags unknown publishers with broad access.

Do I need Jira?

No. Jira is optional for revocation tickets; it can use another tracker you already have, or just hand you the list.

How much does it cost to run?

The template is free. Runs use your Rerun credit.

2,000+ businesses run on Rerun

Hire Coworkers on the ChatGPTplan you already pay for.

  • 1. Plug in your subscription
  • 2. Set up your Coworkers
  • 3. Run your business with Coworkers